


https://store-images.s-microsoft.com/image/apps.29688.2ae9f727-2dd2-4bfb-9502-1b995efff102.11bab43e-c6aa-4b6a-a25a-db5dca5885cb.ac781907-124b-483b-8e4f-a6ed0d16c36d
Salesforce and Microsoft Defender Integration
IT Partner LLC
Just a moment, logging you in...
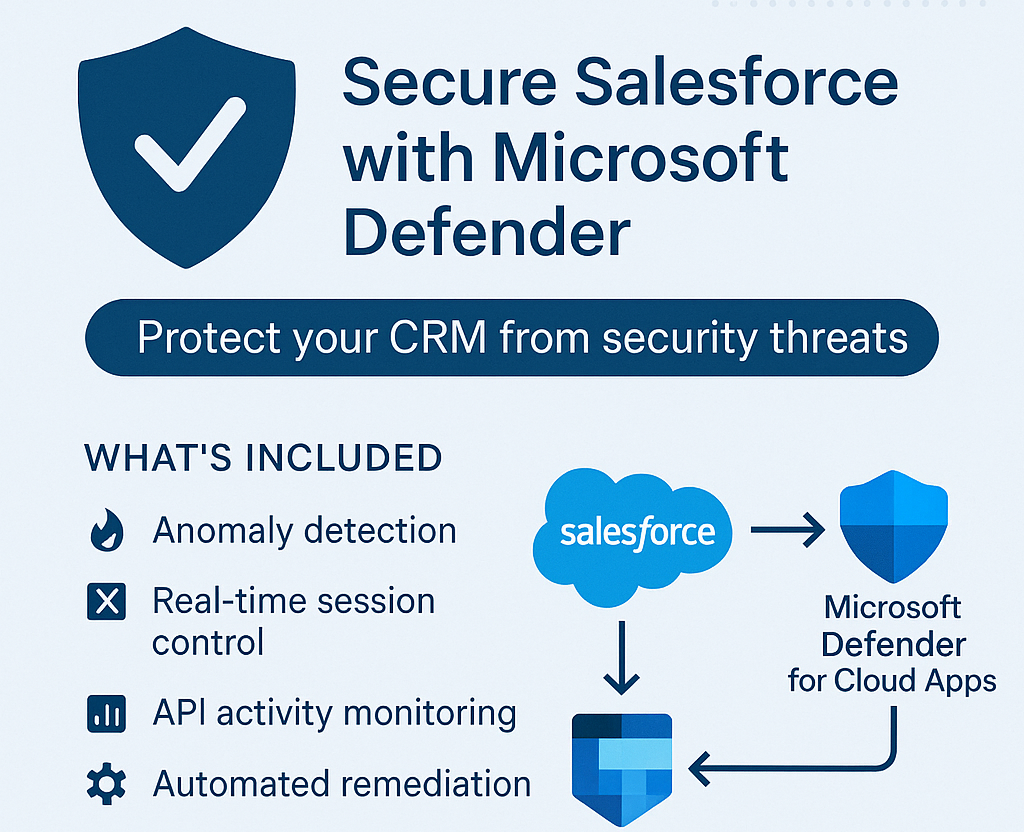
🛡️ Secure Salesforce with Microsoft Defender for Cloud Apps
Concerned about Salesforce account takeovers, unauthorized data exports, or risky sharing?
IT Partner's Salesforce + Microsoft Defender Integration delivers real-time threat protection for your CRM ecosystem.
🔍 What This Integration Does
We connect Salesforce to Microsoft Defender for Cloud Apps and Microsoft Sentinel to enable:
- 🔥 Anomaly detection for suspicious logins, mass exports, or unusual sharing
- 🛑 Real-time session control via Microsoft Entra ID Conditional Access
- 📊 API activity monitoring for unauthorized integrations
- 🔐 Automated remediation through Defender playbooks and Power Automate
- 📜 Compliance auditing with centralized logs in Microsoft Sentinel
💡 Why It Matters
Without Defender integration:
- ❌ Undetected compromised Salesforce accounts
- ❌ Uncontrolled data exports to personal devices
- ❌ No visibility into third-party app access
With Defender integration:
- ✅ Block risky sessions in real-time (impossible travel, anonymous IPs)
- ✅ Detect data exfiltration attempts (mass report exports)
- ✅ Automate responses to security incidents
🚀 Key Benefits
- Gain security visibility over Salesforce activities
- Reduce unauthorized usage and enforce cloud governance policies
- Centralize security alerts and incidents in Microsoft Sentinel
- Automate security responses via Defender playbooks and Power Automate
- Enhance SaaS security compliance (GDPR, HIPAA, ISO 27001)

⚙️ How It Works
API Activity Monitoring
- Track all Salesforce API calls via Microsoft Defender
- Alert on suspicious OAuth token usage or third-party app access
Session Security
- Enforce Entra ID Conditional Access policies (requires SAML SSO):
- Block sessions from Tor/IPs with high attack frequency
- Require compliant devices for
View All Datausers
- Note: UI-based exports require Salesforce Shield for real-time blocking.
- Enforce Entra ID Conditional Access policies (requires SAML SSO):
Threat Response
- Auto-trigger Power Automate flows to:
- Disable compromised accounts
- Revoke suspicious OAuth tokens
- Notify SOC teams via Teams
- Auto-trigger Power Automate flows to:
Sentinel Integration
- Correlate Salesforce events with other security signals
- Generate SOC playbooks for CRM-specific threats
Technical Requirements:
- Salesforce Enterprise/Unlimited + Event Monitoring add-on
- Microsoft Defender for Cloud Apps Plan 2 (for automated remediation)
- Microsoft Entra ID P2 (for risk-based Conditional Access)
- Power Automate Premium (to call Salesforce APIs for remediation)
🎯 Who's This For?
- Companies with sensitive CRM data (financials, PII)
- Security teams using Microsoft Defender and Sentinel
- Organizations requiring SOC 2/GDPR compliance
🏆 Why Choose IT Partner LLC
- Microsoft Security Specialists: Defender + Sentinel certified architects
- Salesforce Security Expertise: 50+ CRM security deployments
- Compliance Ready: Pre-built templates for HIPAA/GDPR
💬 Secure Your Salesforce Environment Today
Protect your CRM data with enterprise-grade security monitoring and automation.
لمحة سريعة
https://store-images.s-microsoft.com/image/apps.28883.2ae9f727-2dd2-4bfb-9502-1b995efff102.11bab43e-c6aa-4b6a-a25a-db5dca5885cb.0e88f5fc-816c-4518-9def-0d16aec990e7